The short answer
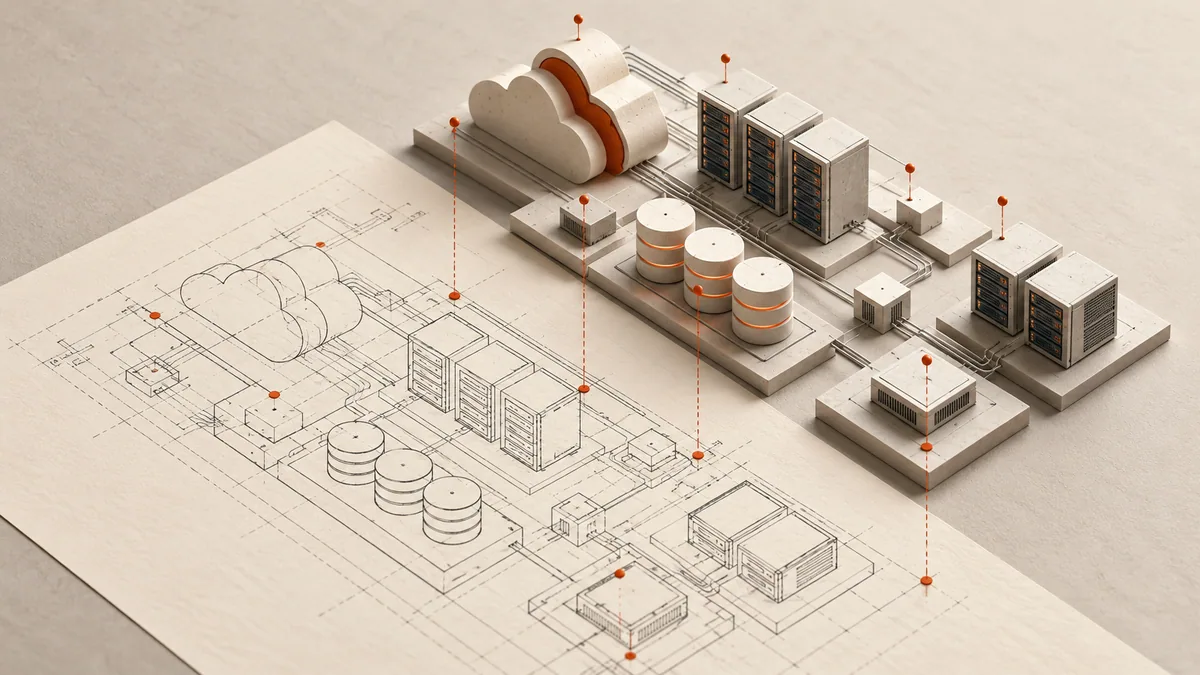
Use infrastructure as code to give agent-requested cloud changes a versioned, reviewable definition. Have agents work through approved modules and inputs, generate a plan, run checks and execute through a controlled identity. Protect state and reconcile drift so the declared configuration remains connected to the resources actually running.
What to take away
- Version infrastructure intent separately from conversational history.
- Protect state and serialize conflicting operations.
- Investigate drift before automatically overwriting live changes.
What does infrastructure as code add to an agent workflow?
A conversation can explain why an environment was requested, but it is a poor sole record of its intended configuration. Infrastructure definitions let a team compare changes, review modules and reconstruct the desired setup independently of the original agent session.
The agent can gather requirements, select an approved module and propose inputs. A deterministic workflow can validate those inputs, generate the plan and execute it. Keep architecture choices and exceptions explicit rather than allowing each request to invent a new resource pattern.
Give agents a bounded configuration surface
Version reusable modules or templates for common environments. Expose the decisions teams actually need to make, such as environment class, region and capacity tier. Validate combinations and explain rejected inputs. Too many free-form options make policy enforcement and future upgrades harder.
Record the selected module version in the environment's operating record. When a template changes, existing environments may need a planned update rather than silently adopting new defaults. Test module upgrades against representative environments and inspect the resource changes they propose.
| Stage | Record to retain |
|---|---|
| Request | Owner, environment and requirements |
| Definition | Module version and validated inputs |
| Plan | Proposed additions, updates and deletions |
| Decision | Policy result and approval when needed |
| Execution | Operation result and resource references |
| Reconciliation | Observed drift and its resolution |
Treat state as sensitive operating data
Terraform state links configuration resources to real infrastructure and can contain sensitive information. HashiCorp recommends appropriate remote storage rather than placing state in version control, with access control and locking support. Protect state from both disclosure and accidental loss.
Concurrent agents can create conflicting operations if they act on the same environment without coordination. Use the backend's supported locking and an operation queue or equivalent control where appropriate. Define how an interrupted lock is investigated; force-unlocking without understanding an active execution can create another failure.
Reference: source 1
Reconcile drift deliberately
Drift occurs when live resources differ from the intended configuration. A person may have made an emergency change, a controller may manage a field or a resource may have been altered outside the normal workflow. A detected difference should lead to a decision about the intended state.
Do not assume every difference should be automatically reverted. Preserve the context of emergency actions and identify who owns the decision. Update the definition, import an existing resource where appropriate or restore the approved state through a reviewed operation. Keep the resolution visible so the same drift does not recur unexplained.
Keep the reviewed plan connected to execution
Generate the plan against the intended environment and inspect replacements, deletions and permission changes. If approval is required, bind it to that proposal. Re-evaluate material changes rather than executing a newly generated plan under an old decision.
After execution, verify the workload and resource inventory. A completed infrastructure command does not prove the application is healthy. Test repeated requests and partial failures so an agent can reconcile status without creating duplicate environments. Latifold's design keeps a centrally versioned resource model while respecting Terraform, OpenTofu, CloudFormation and CDK ownership. Existing IaC changes should use their owner's workflow. New repository IaC files are not required for initial read-only discovery, and JSON/YAML portability is planned.
Common questions
Can an AI agent write Terraform?
It can propose definitions, but generated configuration still needs validation, a reviewed plan where required, appropriate execution permissions and post-change verification.
Should Terraform state be committed to Git?
HashiCorp advises against state storage in version control or storage without suitable locking and secure access controls. Use an appropriate protected backend for your workflow.
Sources & context
References checked on 18 October 2026. Implementation recommendations and illustrative examples are Latifold editorial guidance.
- HashiCorp Terraform: state
State's role, remote storage, access and locking considerations. The agent workflow and drift decision process are practical guidance.
Prepared with AI assistance for Latifold. Verify technical details against your environment and the linked documentation. See our editorial approach.