The short answer
Reliable cleanup of ephemeral environments needs an owner, an expiry time, an inventory and a reconciliation process. Trigger teardown when work ends, then separately check for expired and partially deleted resources. A successful application deletion does not prove that volumes, snapshots, addresses, logs and stored files are gone.
What to take away
- Create lifecycle metadata when resources are provisioned.
- Treat teardown as a tracked operation with failure states.
- Reconcile actual resources against the environment record.
Why temporary environments become permanent costs
A preview is created for a branch, a test or an agent task. The branch closes, but its teardown event is missed. A database deletion fails because a dependency remains. A retained volume or snapshot keeps accruing cost after the application disappears. Each case can look complete in the review interface while cloud resources remain.
Treat environment lifecycle as a system responsibility rather than a reminder to the developer. The creator may no longer be available, the agent session may end and the original automation may fail. The inventory and cleanup policy must outlive all three.
Give every environment a lifecycle record
Create a durable record containing environment ID, project, owner, source reference, creation time, expiry and expected resources. Attach matching labels or tags where the provider supports them. For resources without suitable metadata, maintain an explicit association in the environment inventory.
Define how expiry can be extended and who can approve an exception. A temporary environment supporting an active review may need more time, but extensions should be visible and bounded. Protect production through explicit classification and separate authorization; do not infer that an untagged resource is safe to delete.
| Field | Purpose |
|---|---|
| Environment ID | Join resources to one lifecycle |
| Owner and project | Assign accountability and cost |
| Source reference | Explain why the environment exists |
| Expiry | Define when review or cleanup is due |
| Resource inventory | Find dependencies and leftovers |
| Retention exception | Protect deliberately retained data with an owner |
Delete in a dependency-aware sequence
Stop new work and mark the environment as closing. Identify active jobs, data that must be retained and dependencies that affect deletion order. Revoke temporary access, remove application services and delete associated resources according to the approved retention policy.
Record each step and its outcome. A partial failure should leave the environment in a visible cleanup-needed state, with a retry or an owner. Avoid reporting success while a deletion request is merely pending. Verify resource absence or an explicit retained state after the provider completes its operation.
Use reconciliation as the safety net
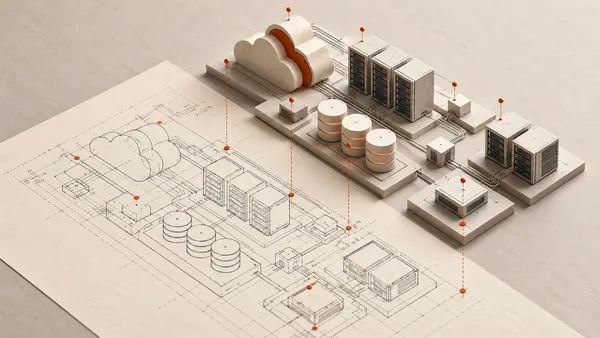
A separate process should compare active environment records with actual cloud resources. It can find expired environments, orphaned resources and incomplete cleanup. Begin with reporting and dry-run review until matching rules are proven, then automate only the well-defined deletion cases.
Google Cloud's resource-usage guidance includes identifying idle and unused resources as part of cost optimization. For preview lifecycles, make that review specific: resource age alone is not enough. Check ownership, environment classification, dependencies and retention before taking action.
- List environments past expiry and approved exceptions.
- Compare the expected inventory with provider resources.
- Classify active, orphaned, retained and uncertain resources.
- Apply policy to proven cleanup candidates.
- Escalate uncertain cases and verify the final inventory.
Reference: source 1
Measure cleanup success, not just deletion attempts
Track time from expiry to verified cleanup, failed teardown operations and cost attributed to expired environments. Review recurring leftovers by resource type. A repeated volume-retention problem calls for a template fix, not a recurring manual deletion task.
Test a missed close event and a deliberately failed deletion in an isolated environment. Confirm the reconciliation process finds both and that production resources remain outside its authority. Latifold's proposed ownership model separates observation from authority to remediate or delete. Verify supported discovery and execution paths, and agree retention and cleanup boundaries before delegating resource creation to agents. A detected orphan is not permission to remove a resource owned by another workflow.
Common questions
Is deleting the preview application enough?
Often it is only part of teardown. Check databases, volumes, snapshots, addresses, stored files, credentials and log retention associated with the environment.
Should cleanup delete every old untagged resource?
No. Unknown ownership is a reason to investigate. Automated deletion should require a proven environment association and an applicable retention policy.
Sources & context
References checked on 18 October 2026. Implementation recommendations and illustrative examples are Latifold editorial guidance.
- Google Cloud: optimize resource usage
Idle and unused resource management as a cost practice. The preview lifecycle and reconciliation process here are implementation guidance.
Prepared with AI assistance for Latifold. Verify technical details against your environment and the linked documentation. See our editorial approach.